Fake Minecraft Mods Are Spreading Malware: How to Download Addons Safely in 2026
Last reviewed 1 November 2026 against McAfee Labs' WeedHack reports, BleepingComputer, the fractureiser investigation and the Modrinth and CurseForge disclosures.
- Start on a trusted platform
- Follow the creator's own link
- Check the file type
- Scan it on VirusTotal
- Keep your antivirus on
You watched a video that promised a free hacked client, clicked the link in the description and ran the file. A day later your Discord is sending odd links to friends, or your Minecraft account email has changed. Maybe you are a parent who just read about WeedHack and wants to know if the mods on your child’s computer are a danger.
Both worries are fair, because criminals spent 2026 hiding password stealers inside Minecraft downloads. This guide gives you the short answer first, then the verified facts, a fair comparison of download sites and a clear recovery plan. Every figure below comes from the original security reports, so you can deal with fake Minecraft mods malware using facts instead of rumours.
Key facts
- Biggest 2026 case
- WeedHack, active since January 2026
- Total hits
- 116,464 (McAfee Labs)
- Malicious files
- More than 3,820 JAR files
- Spread through
- YouTube links and lookalike sites
- Price to criminals
- From $5 a month
Are Minecraft Mods Safe? The Short Answer
Most mods are safe when they come from a moderated platform and the official creator page. The danger comes from copies: cloned websites, YouTube description links, Discord files and “cracked” or free versions of paid cheat clients. Almost every big Minecraft malware case so far started with one of those.
The file type tells you a lot about the risk. Use these quick rules before any download:
- Java Edition mods (.jar files) can run any code on your PC, so only get them from CurseForge, Modrinth or a creator page those sites link to.
- Bedrock addons (.mcaddon and .mcpack files) are game packs, but fake “installers”, “.exe” launchers and APK files are not, so never run one.
- Never switch off your antivirus because a download page or a video tells you to.
- If you already ran something suspicious, jump to the recovery steps below and change your passwords from a different device.
What Is WeedHack? The Fake Minecraft Mods Malware Campaign of 2026
WeedHack is a malware as a service operation that McAfee Labs exposed in its report Game Over: WeedHack, published on 2 June 2026. It disguises itself as real Minecraft clients, mods and tools, and it has been active since January 2026. Anyone can sign up, build an infected mod and spread it, which is why it grew so fast.
WeedHack Key Figures
| Detail | Verified figure |
|---|---|
| Campaign type | Fake Minecraft mods malware sold as a service |
| Active since | January 2026 |
| Report date | 2 June 2026 (McAfee Labs and BleepingComputer) |
| Total hits | 116,464 (McAfee calls them hits; BleepingComputer reports them as infected systems) |
| New hits per day | About 2,000 to 3,000 |
| Unique malicious JAR files | More than 3,820 |
| Distribution URLs | More than 240 |
| Price | Free tier; premium from $5 a month or $24.99 for lifetime access |
| Top countries | United States first, then Germany, India and the United Kingdom |
BleepingComputer’s report by Bill Toulas, also from 2 June 2026, repeats the same core numbers from McAfee telemetry. McAfee adds that 10 domains hosted the dashboard and later payloads, and that the seller’s Telegram channel had more than 850 members before it was taken down.
How WeedHack Spread Through YouTube and SEO Poisoning
The campaign used two main roads, and both rely on trust. The links show up exactly where players already look for mods.
YouTube Description Links
Attackers uploaded Minecraft videos with download links in the description and pinned comments. Some used real voice overs to look genuine, and one passed 7,500 views. Comments often told viewers that a Windows security warning was “normal” and safe to ignore.
SEO Poisoning and Lookalike Sites
The criminals picked clients and mods that have no official website and live only on GitHub, then built polished fake sites that rank in search results for those names. Impersonated names included Meteor Client, Wurst, LiquidBounce, Aristois, Impact, Future and Phobos. One fake site copied the Skytils project and even linked to its real GitHub and Discord to look trustworthy.
What WeedHack Steals
Even the free version is a full infostealer. According to McAfee, it takes:
- Minecraft session IDs and data from four Minecraft launchers
- Saved passwords and cookies from 36 web browsers
- Data from 56 browser crypto wallets and 12 desktop wallet apps
- Discord, Steam and Telegram logins
- Screenshots, system details and files that match 24 search keywords
The premium version adds webcam access, a keylogger, a remote shell, live screen control with mouse and keyboard, and file upload and download. In plain words, a paying customer can watch and control the victim’s PC.
The $5 Subscription Model and the Cyberbullying Problem
WeedHack’s price is the scary part. Premium starts at $5 a month, a lifetime plan costs $24.99, and payment goes through Bitcoin or Litecoin with a new wallet for every payment. The dashboard includes tutorials, a leaderboard of “hits” and a builder that injects the stealer into mods for Minecraft 1.21.0 to 1.21.11.
McAfee found that many customers appear to be teenagers who use the remote access tools to threaten and harass other players. Some recorded victims through their webcams and posted the clips in the Telegram channel. That is why this story matters to parents as much as to players.
WeedHack After the Takedown
On 20 August 2026 McAfee published a follow up called WeedHack Returns. Its original command server and dashboard were down, but infected files kept spreading through fake sites and file hosts. McAfee’s WebAdvisor blocked more than 6,300 visits to those sites in a single month.
The new lures included fake pages for Glazed Client, Radium Client, Xenon Client, SeedCrackerX and Nova Client, a Bedrock client with no official site. For Xenon Client, the top two Google results led to infected downloads. Of the malicious links McAfee tracked, 49.6% were Discord links, 23.4% MediaFire, 8.2% GitHub and 4.6% Dropbox, and some files on Planet Minecraft and EndMods also carried the stealer.
How the Infection Works
The first file, for example “DonutDupe.jar”, hides its window and reads its command server address from an Ethereum smart contract, a trick that is hard to block. Later stages bypass the Windows admin prompt, add 13 folder and 15 process exclusions to Microsoft Defender, and finally exclude the whole C:\Users folder. Persistence comes from scheduled tasks named JavaSecurityUpdater and JMonitoringTask, plus a backdoor disguised as RuntimeBroker.exe.
Earlier Minecraft Malware Incidents
WeedHack is the biggest case so far, but it is not the first. Minecraft is the most used lure for attacks on young gamers: Kaspersky counted 3,094,057 attack attempts using Minecraft between July 2023 and June 2024, almost twice the figure for Roblox.
Fractureiser (2023): Compromised CurseForge and Bukkit Uploads
Fractureiser was uncovered in June 2023, on the morning of the 1.20 release. Attackers took over creator accounts and projects on CurseForge and dev.bukkit.org, so the infected files sat on trusted sites. The fractureiser investigation team says the earliest bad jars date to mid April 2023 and that CurseForge counted about 6,000 downloads of infected files.
It hit Windows and Linux, spread to other .jar files, swapped crypto addresses on the clipboard and stole browser, Discord, Microsoft and Minecraft logins. On Windows, a hidden “Microsoft Edge” folder (with a space) inside %localappdata% meant a full infection.
Windows Borderless on Modrinth (2024)
In May 2024 a mod called Windows Borderless passed Modrinth’s review with a clean file on 30 April, then received malicious updates from 2 May. Modrinth’s public disclosure says about 372 distinct IP addresses downloaded the bad files and one Discord account was stolen before staff removed it within minutes of a report. The lesson is that trusted platforms are safer, not perfect.
Stargazers Ghost Network (2025)
In June 2025 Check Point Research described about 500 GitHub repositories pushing fake Forge mods named after cheat tools such as Oringo and Taunahi, with more than 1,500 hits on the attacker’s Pastebin pages. The loader was missed by every antivirus engine on VirusTotal when it was found.
Fake Mod Apps on Google Play (2017 to 2023)
Mobile players have their own history. ESET found 87 fake Minecraft mod apps with up to 990,000 installs in 2017, and Kaspersky found more than 20 more in 2020. In April 2023 McAfee reported 38 Minecraft style games, installed by at least 35 million people, that loaded hidden ads in the background.
Discord Modpack Scams (2026)
In May 2026 the CurseForge blog described a scam where a stranger on Discord asked a player to help record a video on a private server. The “required modpack” was a tiny ZIP holding a file called EchoVoiceBeta-1.0-SNAPSHOT.jar that could run commands and download more malware. CurseForge added a warning for suspicious files on import and a “CurseForge Files Only” option.
Change your passwords from a clean device such as your phone. A stealer on the PC can capture new passwords as you type them.
Red Flags: How to Spot a Fake Mod Download Page
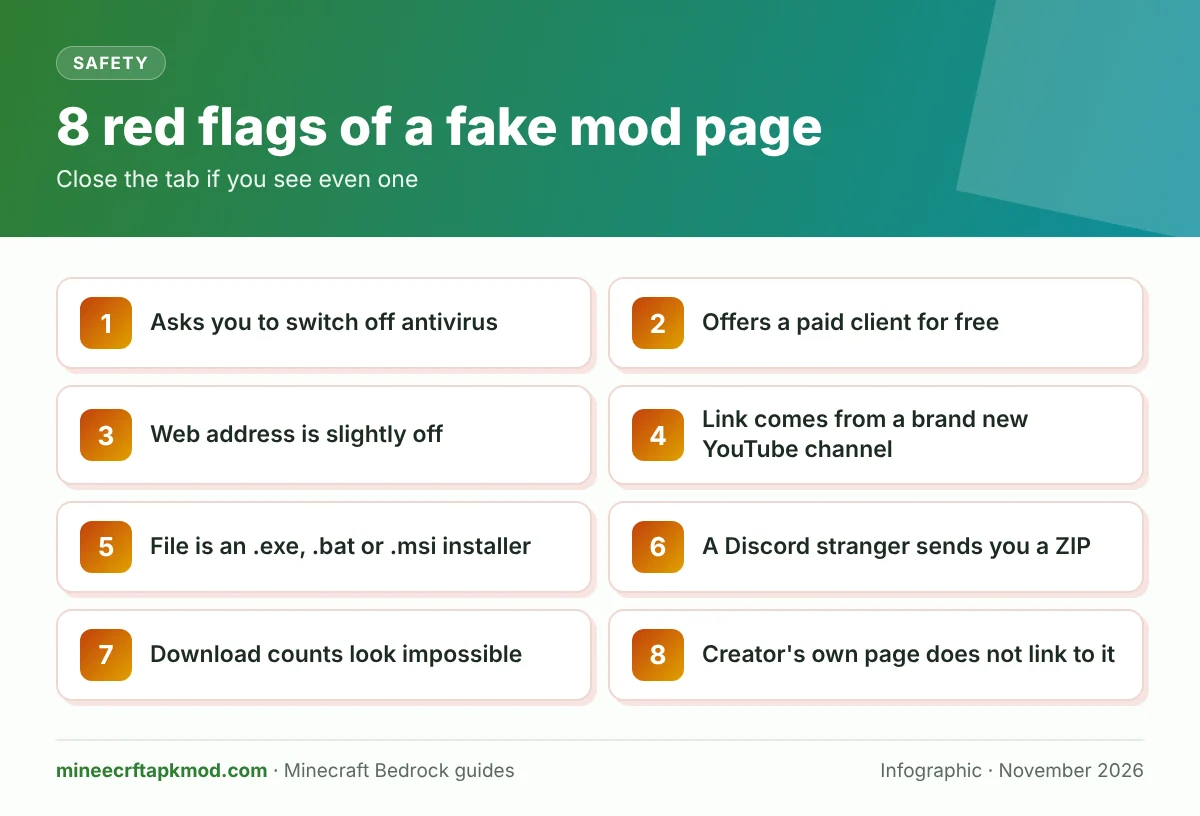
Fake pages look polished in 2026, so judge them by behaviour, not design. If you see even one of these, close the tab:
- The page asks you to disable antivirus or Windows Defender “because of a false positive”.
- A paid client is offered free, “cracked” or “unlocked”.
- The domain is slightly off, such as an extra letter, “clients” instead of “client”, or a free builder address like lovable.app or github.io for a project that has a real site.
- You arrived from a new YouTube video on a channel that only posts download videos, the classic route for fake Minecraft mods malware.
- The file is an .exe, .bat, .scr or .msi “installer” when a mod should be a .jar (Java) or .mcaddon, .mcpack or .mcworld (Bedrock).
- A Discord stranger sends you a ZIP and rushes you to install it.
- Download counts or reviews look impossible, such as “10 million downloads” on a site nobody has heard of.
- The page claims to be “official” but the creator’s GitHub, CurseForge or Modrinth page does not link to it.
A Minecraft virus mod rarely announces itself, but the page that delivers it usually does. One red flag is enough reason to leave.
Safe Minecraft Mod Sites Compared
No site can promise zero risk, but some check every file and some check nothing. Here is a fair view based on each platform’s own published rules and the incident reports above.
| Download source | Edition | What checks exist (sourced) | Known problems | Safety rating |
|---|---|---|---|---|
| Minecraft Marketplace | Bedrock | Mojang says every new submission is reviewed for quality and suitability before release | None of the reports above involve Marketplace content | Safest |
| CurseForge (site or app) | Java and Bedrock | Files are decompiled, hash checked, scanned and escalated to manual review (since 2024) | Fractureiser came through hijacked creator accounts in 2023 | Very safe |
| Modrinth | Java | Scanning plus human review of every new project | Windows Borderless slipped in through a later update in 2024 | Very safe |
| MCPEDL (mcpedl.com) | Bedrock | Automated checks and manual review; .exe files and third party installers are rarely allowed | Downloads often pass through ad link pages; read what you land on | Generally safe with care |
| Creator’s own site or GitHub | Both | Only as safe as your check that the site is genuine | WeedHack cloned sites for GitHub only projects | Safe if verified |
| Random YouTube description links | Both | None | Main WeedHack route | Avoid |
| Discord files and DMs | Both | None; CurseForge cannot scan files friends send | 49.6% of WeedHack links tracked in Aug 2026; ZIP modpack scams | Avoid |
Is CurseForge Safe?
Yes, for files from the official site or app; its 2024 review process decompiles and scans every mod and sends doubtful ones to a person. The risk starts when you import a ZIP from someone else, because CurseForge only scans files from its own servers.
Is Modrinth Safe?
Yes, with one caveat. New projects are reviewed by people, but later updates go live faster, which is how the Windows Borderless case happened, and Modrinth removed it within minutes and published every detail.
Is MCPEDL Safe?
MCPEDL, the long running Bedrock addon hub, says submissions get automated checks and manual review, and its rules ban “downloader” installs on ad links. If a link asks you to install software, stop, and check that the address bar says mcpedl.com, since several sites use similar names.
Minecraft Marketplace
The Marketplace inside Bedrock is the only source run by Mojang. Content from approved partners is reviewed before release and installs straight into the game, with no file for you to open.
Never switch off your antivirus because a download page or video tells you to. Real mod sites never ask for that.
Java .jar Mods vs Bedrock .mcaddon Files: Which Is Riskier?
This difference is the most useful thing a player can learn. Every large Minecraft mod malware case in this guide, from fractureiser to WeedHack, used Java JAR files, while the mobile cases used fake Android apps.
Why a Java JAR Mod Can Run Any Code
A Java mod is a real program that the loader runs with the same rights as your user account. It can read your browser folders, contact any server and download more files, which is exactly what WeedHack and fractureiser did. This is not a flaw in Forge or Fabric; it is simply how Java mods work, so trust in the source is everything. Our Java Edition guide explains the edition itself.
What a Bedrock Addon Can and Cannot Do
A Bedrock .mcaddon is a zipped bundle of behavior and resource packs: JSON files, textures, sounds and, optionally, JavaScript. Microsoft’s documentation shows scripts are declared in the pack manifest and use Minecraft‘s own modules to control entities, blocks and items. The module that sends web requests, @minecraft/server-net, does not work in the game client or in Realms, only on a dedicated server.
So a normal addon has no documented way to read files on your device or send your passwords anywhere. It can still break a world or behave badly, which is why you should back up worlds first. Our guide on how to install addons on Minecraft Bedrock shows the safe way to import packs on every device.
Where Bedrock Players Still Get Caught: Fake Installers, Clients and APKs
The Bedrock risk is anything that is not a pack. A “Bedrock client” like the faked Nova Client is a PC program, an “addon installer.exe” is a program, and a modded Minecraft APK from an unknown site is a full Android app with its own permissions. Get the game only from official stores, as explained in our Minecraft Pocket Edition guide, and only open files ending in .mcaddon, .mcpack, .mcworld or .mctemplate.
How to Check a Minecraft Mod for Viruses Before You Install It
No single check catches everything, so stack a few of them. The whole routine takes about two minutes:
- Start from the platform, not a search result. Open CurseForge or Modrinth directly and search there, or follow the link on the creator’s verified profile.
- Compare the address. Make sure the domain matches the one the creator lists, letter for letter.
- Check the file type. A Java mod is a .jar and a Bedrock pack is .mcaddon or .mcpack; anything else needs a very good reason.
- Upload the file to VirusTotal. A clean result is not proof, since the Stargazers loader passed every engine, but a red result is a clear stop sign.
- Read the history. A project with years of updates, comments and a known author is far safer than one uploaded last week.
- Let your antivirus stay on. If Defender blocks a file, believe it.
For Java mods you already own, scanners built during the fractureiser response, such as Overwolf’s jar infection scanner, check a whole mods folder for that malware. Pick from our list of the best Minecraft mods if you want well known starting points.
Signs Your PC Is Infected or Your Minecraft Account Was Stolen
Stealers are built to stay quiet. Look for these side effects instead:
- Your Discord sends links or “free Nitro” messages you did not write.
- Your Minecraft name, skin or account email changes, or you get logged out of Minecraft and Microsoft.
- Microsoft Defender is switched off or shows exclusions you did not add.
- Task Scheduler shows tasks such as JavaSecurityUpdater or JMonitoringTask.
- Your webcam light turns on by itself, or friends say “you” messaged them at odd times.
Having a Minecraft account stolen is usually the visible part; the stealer has normally taken browser passwords and cookies too. Act on all accounts, not only the game.
What to Do If You Downloaded a Fake Mod
Work through these steps in order. Do the password changes from a clean device, such as your phone on mobile data, because a stealer on the PC can capture new passwords as you type them.
Disconnect and Remove the File
Unplug the network or turn off WiFi on the infected PC. Delete the mod and any launcher it came with, then look in Task Scheduler and Defender exclusions for the entries listed above. Do not log into anything on that PC yet.
Secure Your Microsoft and Minecraft Account
From your clean device, sign in at account.microsoft.com/security, change your password and review recent activity. Use the “Sign me out” option at account.live.com/proofs/manage/additional to end sessions everywhere, which matters because WeedHack steals Minecraft session IDs. If the hacker changed your email, use Microsoft’s account recovery form, then see our guide on how to back up your Minecraft account so a future loss is easier to fix.
Reset Your Discord Token
A Minecraft mod stealing Discord token data lets the attacker log in without your password. Change your Discord password, which is widely reported to issue a new token, then open Settings > Devices and choose “Log out all known devices” to be sure. Check Authorized Apps and remove anything you do not recognise.
Change Other Passwords and Turn On Two Step Verification
Change your email password first, then Steam, Telegram, banking and any crypto wallets, moving funds if a wallet was on that PC. Turn on two step verification with an authenticator app for Microsoft, Discord, Steam and email. Warn friends that messages from your accounts may have been fake.
Scan or Reinstall Windows
Run a full Microsoft Defender scan and a Microsoft Defender Offline scan, and use a second scanner for a second opinion. Because WeedHack installs a backdoor and edits Defender settings, a clean reinstall of Windows is the safest choice after a confirmed infection. Back up only documents, photos and Minecraft worlds, not programs or mods.
A Guide for Parents
If your child plays Java Edition on a PC, ask what clients and mods they use and where they got them. Most WeedHack lures were cheat clients and “dupe” mods for popular servers, so a child who wants an edge in PvP is the main target. On Bedrock, steering them to the Marketplace and moderated addon sites removes most of the risk of fake Minecraft mods malware.
You do not need to be technical to help. These steps make a real difference:
- Give the child a standard Windows account, not an administrator one, so installers need your approval.
- Turn on two step verification for their Microsoft account and keep the recovery email as yours.
- Agree on a rule: no files from Discord strangers or YouTube descriptions, ever.
- Tell them that if anyone claims to have hacked them or threatens them, they should not follow instructions and should come to you first.
McAfee gives that last piece of advice directly, because WeedHack users harassed victims through their webcams. A calm talk works better than a ban, since a child who fears punishment may hide an infection.
Our install guide walks through every device step by step. It also covers the errors you are most likely to see.
FAQ About Minecraft Mod Malware
These are the questions players and parents ask most after reading the WeedHack news. Each answer is short and based on the sources above.
Is WeedHack still active in late 2026?
Its original server and dashboard were taken down, but McAfee’s August 2026 follow up found infected files still spreading through fake sites, Discord, MediaFire, GitHub and Dropbox. Treat it as active and keep avoiding unofficial client downloads.
Can a Bedrock addon steal my Discord token?
A normal .mcaddon or .mcpack has no documented way to reach your files or the internet, because the web request module does not run in the game client. A fake installer, .exe or APK can, so the file type is what matters.
Does antivirus catch fake Minecraft mods?
Often, but not always. The Stargazers loader passed every VirusTotal engine at first, and WeedHack adds its own Defender exclusions, so a source check matters more than a scan.
Will Mojang restore a stolen Minecraft account?
Minecraft accounts now run on Microsoft accounts, so recovery goes through Microsoft’s account recovery form and support. Acting quickly and having recovery details set up beforehand makes a big difference.
Fake Minecraft mods malware works by borrowing trust from YouTube, search results and Discord, so the fix is to borrow trust only from places that earn it: the Marketplace, CurseForge, Modrinth and verified creator pages. If you already ran a bad file, the steps above cover your Microsoft, Minecraft and Discord accounts and your PC, so you can get back to playing without the stealer watching.